Patchstack
Not explicitly stated · Founded 2021 · 51 employees on LinkedIn · 5 known investors
Patchstack is a security platform that helps make open-source software safer. The company serves developers and organizations using open-source projects.
Also known as Patchstack OÜ
Founders & leadership
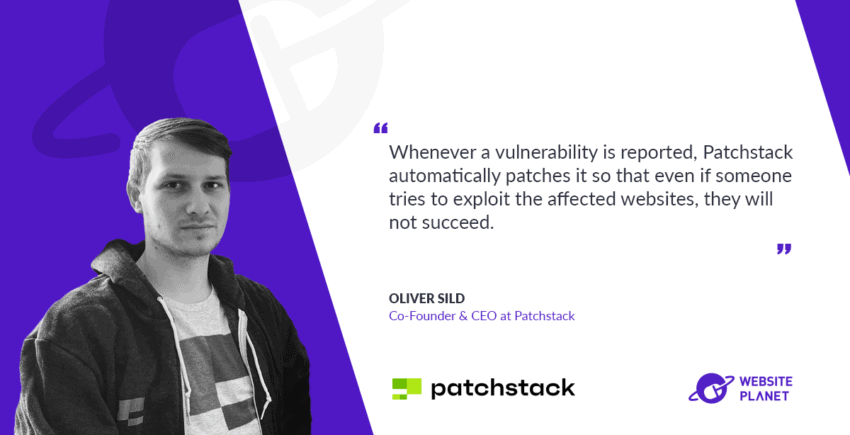
Patchstack was founded in 2021 by Oliver Sild.


Investors · 5
Also in the syndicate · 1
Company profile
researched Aug 2026Patchstack is a security company focused on vulnerability intelligence and mitigation for websites built on open-source software, primarily WordPress and its plugin and theme ecosystem, with recently announced coverage for Node.js applications used by web hosts. Its core product, RapidMitigate, runs inside the website itself rather than at the server layer and deploys targeted mitigation rules that block exploitation of known vulnerabilities without requiring code changes or immediate updates. The company states this approach prevents up to 74% more vulnerabilities from being exploited than leading web application firewalls, and that it maintains over 12,000 (elsewhere cited as 16,720 in its public database) unique mitigation rules. Capabilities include software composition analysis, contextual prioritization based on known exploited vulnerabilities, remote software management, custom protection rules, an IP blocklist module, WordPress-specific hardening, a threat intelligence API, reporting features and support for PCI-DSS 4.0 requirements.
Patchstack operates a public open-source vulnerability database that lists tens of thousands of vulnerabilities in WordPress plugins and themes as well as npm packages, along with triage status and mitigation availability. The company reports it disclosed more than 4,100 vulnerabilities in 2024, published 76% of all known WordPress-related security vulnerabilities in 2023 and became the largest CVE Naming Authority by volume that year. It runs a Zero-Day Bug Bounty Program, which awarded a $14,400 bounty for a critical LiteSpeed Cache plugin vulnerability, and a managed vulnerability disclosure program (VDP) platform developed with the European Union that is free to plugin and theme developers and is positioned to help projects comply with the European Cyber Resilience Act. Around 900-944 plugins installed on millions of sites list Patchstack as a security point of contact.
The team is fully remote and international, led by co-founder and CEO Oliver Sild, with Dave Jong as CTO, Siobhan McKeown as COO, Darius Sveikauskas leading bounty and data, and staff across security research, engineering, marketing, sales, customer success and finance.
Founding story
Co-founded by Oliver Sild, who serves as CEO, together with CTO Dave Jong, whose bio describes starting a software company via Reddit.
Business model
Patchstack sells subscription security software directly and through channel partners. A Developer plan is priced at $69 per month billed annually ($828/year) covering website licenses and three seats, with additional seats at $24 per seat per month and additional bundles of five sites at $12.50 per month. Enterprise and Web host plans use custom billing and add extended API endpoints, SLAs, data processing agreements and dedicated rollout support. Web hosting partners resell or bundle Patchstack as an add-on, which the company positions to them as a new security revenue stream.
Recurring subscription fees per website/seat for individual developers and agencies, custom enterprise contracts, and infrastructure-wide licensing for hosting providers; personal plans are distributed via partners and resellers.
Traction
Public database totals of 51,314 entries with 16,720 mitigation rules; 12,000+ mitigation rules cited on the site; 4,100+ vulnerabilities disclosed in 2024 (13% highly exploitable); exclusive vulnerability intelligence for 944 WordPress plugins and roughly 900 plugins naming Patchstack as security contact. Partner testimonials cite 631,500+ threats blocked in the first month across WP Umbrella sites, prevention of more than 56,000 vulnerabilities in one managed WordPress environment, and protection against 1.3 million vulnerabilities over six months for another partner's users. Product rating cited as 4.9 stars.
Latest developments
Announced expansion of its protection to Node.js applications for web hosts, added remote software management and extended API endpoints to its plans, and closed a $5M Series A in 2024 intended to accelerate product development and build sales and marketing functions.
▸Full profile — market position, technology, go-to-market, geography, history
Market position
Patchstack positions itself as the leading handler of open-source vulnerability intelligence, claiming the largest collection of mitigation rules on the market and the ability to mitigate vulnerabilities up to 48 hours ahead of public disclosure and of competitors that rely on its data. Press coverage describes it as a leading WordPress security company, and it was reported as the largest CVE Naming Authority by volume in 2023, publishing 76% of known WordPress-related vulnerabilities that year.
In-application mitigation rules rather than server-level WAF filtering, allowing context-aware blocking without code changes, tooling conflicts or false positives; the largest published set of mitigation rules; and first-hand vulnerability intelligence sourced from its own CVE Naming Authority operations, bug bounty program and managed VDP, enabling mitigation ahead of public disclosure.
Technology
RapidMitigate combines software composition analysis for deep application visibility, threat intelligence and context-aware prioritization based on known exploited vulnerabilities to deploy on-demand mitigation rules. Unlike a traditional web application firewall running at the web server, RapidMitigate executes within the website and can use application context such as user authorization and software versions, which the company says reduces resource usage and false positives. Additional components include an IP blocklist module, WordPress hardening, WP-CLI installation support, CI readiness checks, API integrations, real-time SCA snapshot reports and data retention of up to 24 months.
Go-to-market
Direct sales (contact sales and self-serve pricing with a first-month-free offer and 30-day money-back guarantee) combined with an extensive partner channel: roughly 20 official security partners that offer Patchstack protection as an add-on and around 14 vulnerability monitoring partners that use Patchstack threat intelligence to alert their customers. A free managed VDP platform for plugin and theme developers and a public vulnerability database serve as community and top-of-funnel channels.
Web developers, agencies and professionals maintaining WordPress sites; MSPs and businesses needing advanced security and compliance; and web hosting providers deploying protection across their infrastructure, including eCommerce/WooCommerce sites subject to PCI-DSS 4.0.
Geography
Operates as a full-remote, global team; partnerships with hosting providers and collaboration with the European Union and the European Innovation Council indicate a significant European presence.
History
In 2022 the company received a €2.7M R&D grant from the European Innovation Council. In 2023 it published 76% of all known WordPress-related security vulnerabilities and became the largest CVE Naming Authority by volume. In 2024 it was selected for Google's AI for Cybersecurity accelerator program, its bug bounty program paid a record $14,400 bounty for a LiteSpeed Cache vulnerability, and it raised a $5M Series A led by Karma Ventures, G+D Ventures and Emilia Capital. It has since extended protection to Node.js applications for web hosts.
Compiled by commissioned research from 8 cited public sources — announcements, filings, and press listed under research sources below.
Key figures
latest reportedCompany-reported or press-reported figures, each dated to when it was claimed — not independently audited.
Competitors · 3
by search overlap

Companies competing with Patchstack for the same Google search keywords, organic and paid, via search-intersection analysis.
Timeline · 7
launches, deals, and filingsPatchstack announced it is now securing Node.js applications for web hosts.
Patchstack raised a $5 million Series A round led by Karma Ventures, G+D Ventures and Emilia Capital, an investment firm backed by Yoast founders Marieke van de Rakt and Joost de Valk. CEO Oliver Sild said the capital would accelerate product development and build a sales and marketing team.
$5M source ↗
Patchstack's Zero-Day Bug Bounty Program awarded the highest bounty in WordPress history, $14,400, to John Blackbourn for a critical vulnerability in the LiteSpeed Cache plugin.
$14.4K source ↗
Patchstack was selected by Google for its AI for Cybersecurity accelerator program, leveraging its dataset of open-source security vulnerabilities.
Patchstack's managed vulnerability disclosure program platform, developed in collaboration with the European Union, is free for plugin and theme developers and helps projects comply with the upcoming European Cyber Resilience Act.
Patchstack published 76% of all known WordPress-related security vulnerabilities in 2023 and became the largest CVE Naming Authority by volume that year.
Patchstack received a €2.7M research and development grant from the European Innovation Council.
Dated company events from announcements, filings, and press; legal rows summarize public dockets and regulator releases.
In the news
▸Research sources · 8
primary sources listed
- Patchstackpatchstack.com · web
8 public sources were cited for this profile; the first-party ones are listed here.
Frequently asked questions
- What does Patchstack do?
- Patchstack provides vulnerability intelligence and automated mitigation for WordPress and other open-source web software.
- Who founded Patchstack?
- Patchstack was founded by Oliver Sild in 2021.
- Who are Patchstack's investors?
- Patchstack's investors include Karma Ventures, Specialist VC, Thorgate Ventures, Trind Ventures.
- Where is Patchstack headquartered?
- Patchstack is headquartered in Not explicitly stated.